Why Teams Adopt AI Faster When Boundaries Are Visible
AI product adoption speeds up when users can see what AI can access, change and remember. Learn the boundary signals that reduce trust drag.
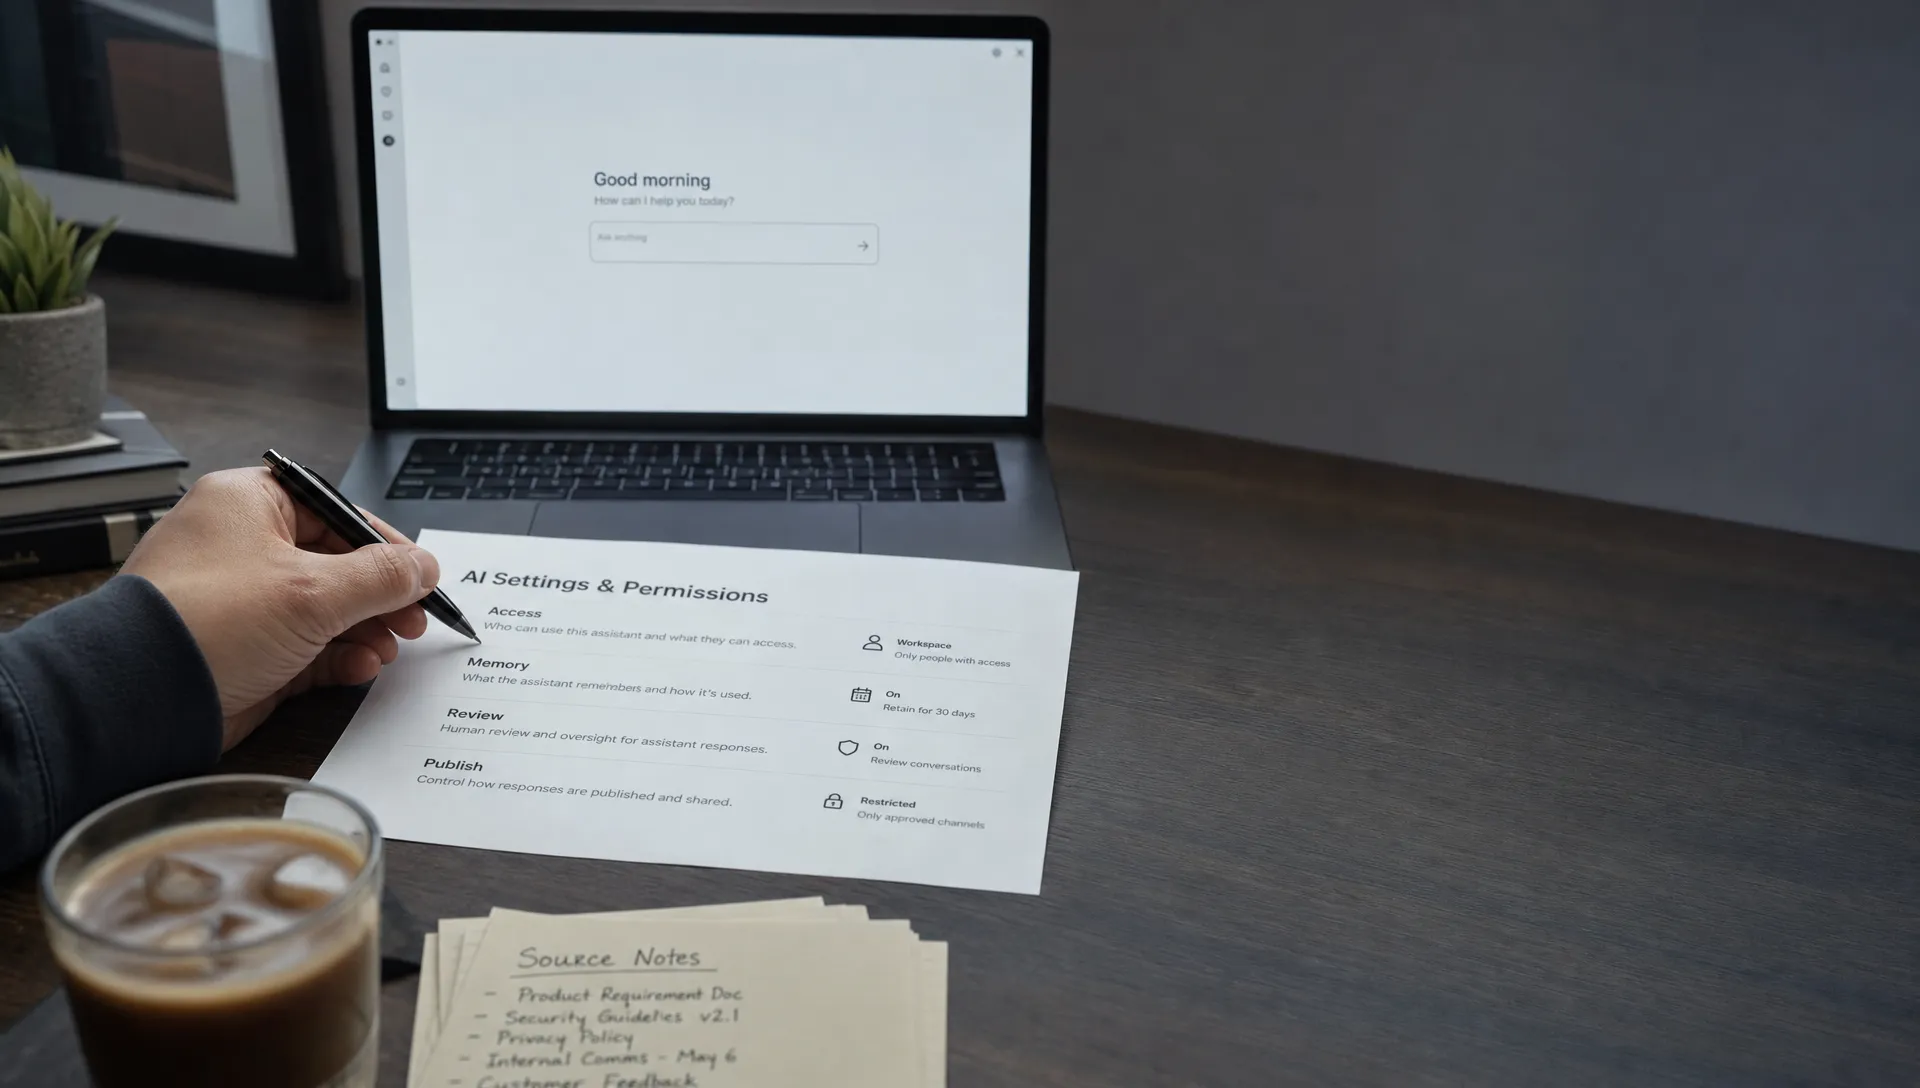
When AI product adoption stalls, teams often blame the model or the launch plan. The quieter problem is usually simpler: users try the feature in a harmless corner, praise the demo then keep it away from real work. They cannot see where the AI stops.
That uncertainty creates drag. A user who does not know what the AI can read, change, remember or send has to invent their own safety rules. In a team setting, that slows everyone down. Nobody wants to be the person who let an assistant touch the wrong account, rewrite the wrong customer message or leak the wrong context.
Visible boundaries do not make AI feel less capable. They make it easier to use.
The symptom: the AI stays in the sandbox
You can spot a boundary problem before users say the word “trust.” It shows up as contained usage.
People use the AI on drafts but not customer-facing work. They ask it to summarize public docs but not internal decisions. They generate ideas but do not let those ideas enter the workflow. They copy the output into another tool, edit it heavily then publish from somewhere else.
This is not always a quality issue. The output may be useful. The problem is that the user cannot predict the blast radius of using it.
In B2B products, adoption is a social behavior. A single user may understand the feature, but the team still needs shared confidence around what is safe. If the boundary is invisible, every user has to negotiate that safety alone.
That is slow. It is also exhausting.
Why visible boundaries speed up AI product adoption
Visible boundaries speed up AI product adoption because they reduce the number of private questions a user has to answer before acting.
A good boundary answers questions like these before the user gets anxious:
- What data can the AI access right now?
- What can it change without approval?
- What will be remembered after this session?
- Who can see the input, output and history?
- What happens if the AI is wrong?
These are product questions, not just policy questions. If the answers live only in a help center, they will not shape behavior at the moment of use.
The boundary has to appear where risk is felt. Before generation, users need to know what context is included. During review, they need to know what changed. Before publish, send or save, they need to know whether they are still in control.
Teams adopt faster when the product makes that control obvious.
What boundary ambiguity looks like in product data
Boundary ambiguity rarely announces itself cleanly. Users do not open a feedback form and write, “Your permission model is unclear.” They route around the feature.
| Product signal | Likely boundary problem | Better response |
|---|---|---|
| High first-use rate, low second-use rate | Users tried it but did not feel safe repeating it | Add visible scope, review and rollback states |
| Many generations, few accepted outputs | Users cannot tell whether output is safe to use | Show sources, diffs, assumptions or confidence cues |
| Heavy prompt disclaimers from users | Users are trying to create missing guardrails manually | Move constraints into product controls |
| Frequent undo after AI action | The AI acted beyond the user's expected boundary | Add confirmation before high-impact actions |
| Admins disable the feature after pilot | Team-level risk is unclear | Expose workspace controls, audit trail and data use rules |
The table matters because AI product adoption fails differently from normal feature adoption. A normal feature might fail because users do not see value. An AI feature can fail after users see value, because the path from value to safe action is unclear.
If your data shows curiosity without commitment, do not start by adding more onboarding. Start by asking which boundary the product hides.
Boundary visibility is not a legal page
A legal page may satisfy procurement. It does not help a user decide whether to run the AI on a sensitive deal note at 4:55 p.m.
Boundary visibility belongs inside the workflow. It should be close to the button, panel, editor or agent action where the user is making a risk decision.
The access boundary
The access boundary tells users what the AI can see.
This is where many products create accidental anxiety. A text box says “Ask AI anything,” but the user does not know whether “anything” includes the current document, the whole workspace, connected apps, customer records or previous conversations.
Make scope explicit. “Using this page only” feels very different from “Using all workspace knowledge.” If users can expand scope, show the tradeoff before they do it.
For a deeper treatment of what happens when users cannot define a safe operating area, the related piece on setting a safe boundary for AI trust covers the privacy and control side in more detail.
The action boundary
The action boundary tells users what the AI can do.
There is a large difference between suggesting a reply, drafting a reply, scheduling a reply and sending a reply. Teams often blur these steps because they want the AI to feel powerful. That creates the opposite effect. Users pull back.
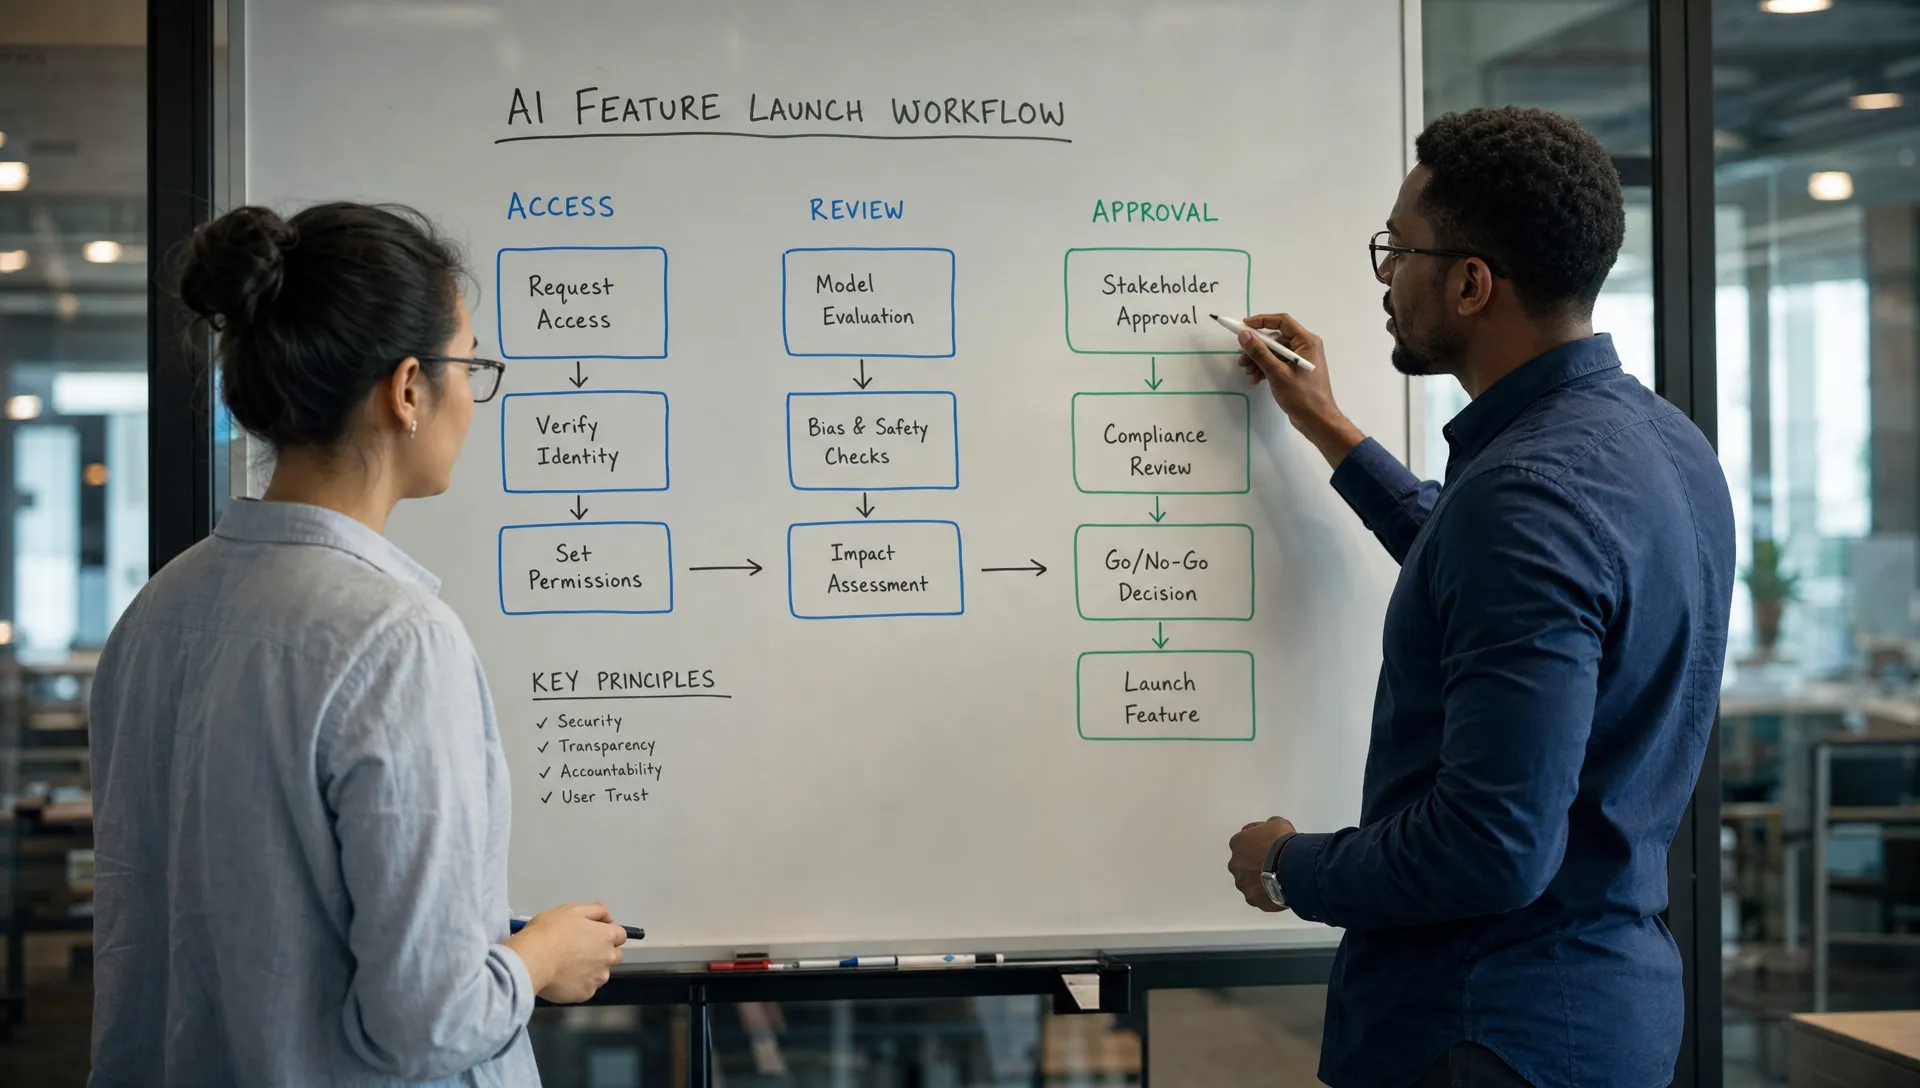
A reliable pattern is to separate low-risk assistance from high-impact action. Let the AI draft, classify, summarize or recommend freely when the user can inspect the result. Require review before changes that affect customers, billing, permissions, production data or shared records.
This is why AI that acts too early can be adoption-negative. If that is your symptom, the breakdown is close to the one described in the trust cost of AI acting too soon.
The memory boundary
The memory boundary tells users what the system retains.
Memory can be useful. It can also feel invasive when users do not understand it. If the AI remembers preferences, instructions or prior work, say so. If a conversation will not be used later, say that too.
Do not rely on vague labels like “personalized.” Tell users what is stored, where they can review it and how to delete or reset it. In team products, separate personal memory from shared workspace memory. Mixing those two creates political risk, not just UX friction.
The confidence boundary
The confidence boundary tells users how far to rely on the output.
This does not mean every AI response needs a numeric confidence score. Often, better signals are more practical: sources, changed sections, missing information, assumptions, known limitations or a clear “review required” state.
The goal is not to make the AI sound uncertain. The goal is to tell the user where judgment is still required.
What known products get right
Grammarly works partly because its boundary is legible. It suggests edits. The user accepts, dismisses or rewrites. The system may be proactive, but the final text remains under user control.
GitHub Copilot also benefits from a visible action boundary. It can suggest code inside the editor, but the developer reviews, accepts, modifies and tests before that code becomes part of the product. The boundary is not perfect, but it is familiar: suggestion before commit.
Perplexity makes verification more visible by attaching sources to answers. Sources do not guarantee correctness, but they give users a path to inspect the claim instead of treating the answer as a sealed black box.
Cursor and other AI coding tools expose another important pattern: diffs matter. When AI changes files, users need to see what changed before they accept it. The more the AI moves from suggestion to agentic action, the more visible the boundary has to become.
These patterns work because they make the user’s role clear. Use accelerates when people know where their responsibility begins and ends.
Decisions to make before adding more onboarding
If AI product adoption is blocked by unclear boundaries, onboarding copy will not fix it. You need product decisions.
Start with these:
- Define the default data scope for each AI action.
- Decide which actions require confirmation.
- Separate draft, save, publish and send states.
- Show what the AI changed, not just what it produced.
- Give users a clear undo or rollback path.
- Make memory visible, editable and removable.
These decisions are more useful than another tooltip explaining that the AI is “there to help.” Users already understand the promise. They need to understand the operating limits.
A simple diagnostic question helps: what could the user reasonably fear this AI might do?
If the product does not answer that question in the interface, the user will answer it pessimistically.
Metrics that confirm a boundary problem
Look for hesitation after value appears. That is the fingerprint.
Strong generation rates with weak acceptance rates suggest review friction or unclear confidence. Strong individual use with weak team rollout suggests admin or policy uncertainty. Heavy editing after generation may mean the output is close but not safely usable. Long prompts full of constraints often mean users are building guardrails the product should provide.
Support tickets are useful too. Questions like “Can it see all my files?” or “Does it train on this?” are not edge cases. They are adoption blockers stated plainly.
The fix is not to promise perfect safety. The fix is to make the product’s actual boundary visible enough that users can make a grounded decision.
Frequently Asked Questions
What is a visible boundary in an AI product? A visible boundary is an in-product signal that shows what the AI can access, change, remember or publish. It helps users understand the safe operating area before they rely on the output.
Why do visible boundaries improve AI adoption? They reduce uncertainty. Users move faster when they know the AI will not cross into sensitive data, irreversible actions or shared workflows without clear consent.
Are boundaries the same as permissions? No. Permissions control what is allowed. Boundaries explain what is happening in the moment. A product can have correct permissions and still feel unsafe if users cannot see them.
Should every AI action require confirmation? No. Low-risk suggestions can stay lightweight. High-impact actions, such as sending, deleting, publishing, updating records or changing permissions, usually need explicit review.
A practical next step
If your AI feature gets trial but not repeat use, map the stalled moment to a boundary. Ask whether the user lacks clarity about access, action, memory or confidence.
For a faster read, run the symptom through the free AI adoption triage tool. If you want a deeper operating system for diagnosing these breaks, the AI Product Adoption Deck turns patterns like this into diagnostic cards, action cards and workshop templates your team can use on the actual product surface.