Why Users Paste Sensitive Data Despite Your AI Privacy Controls
AI privacy controls not stopping sensitive pastes? Diagnose risky workflows and design safer input paths without blocking useful work.
Users tick the privacy acknowledgment, then paste a customer transcript containing names, account details and internal notes. Your AI privacy controls are visible. The behavior barely changes. Meanwhile, activation looks healthy because people are completing the task. This is an AI product adoption problem that a usage dashboard can miss: the feature is useful, but the easiest route to value may involve data your policy does not permit.
Before adding another warning, identify what users believe the control does and what their task requires.
Diagnose the mismatch before blaming the user
A sensitive paste is not automatically a policy violation. Some products are approved to process certain sensitive information under defined conditions. Start by specifying which data is permitted, for which task and through which processing path.
If those decisions are unresolved, first work through the privacy decisions product teams need to make early. This diagnosis assumes rules exist but are not reliably shaping behavior.
Separate what the user knows from what the product enforces:
| Observed symptom | Possible mechanism | What to check |
|---|---|---|
| Users paste full transcripts | Useful context and sensitive fields arrive together | Can the task succeed with a smaller excerpt? |
| Users cite “not used for training” | They interpret one assurance as blanket permission | Can they explain processing and retention separately? |
| Users dismiss every warning | Alerts do not distinguish meaningful risk | How often do permitted inputs trigger warnings? |
| Users switch from upload to paste | Controls cover one input path only | Do attachments, clipboard input and integrations follow the same rules? |
| Users abandon after a block | No permitted route completes the task | What can they actually do next? |
These are hypotheses to test, not labels to assign from analytics alone.
Why a careful user still pastes the whole document
The product rewards completeness
“Add more context” is common AI guidance. Users may also learn through experience that short prompts produce vague answers. If removing identifiers requires manual editing, the product has made safer use more labor-intensive than unrestricted use.
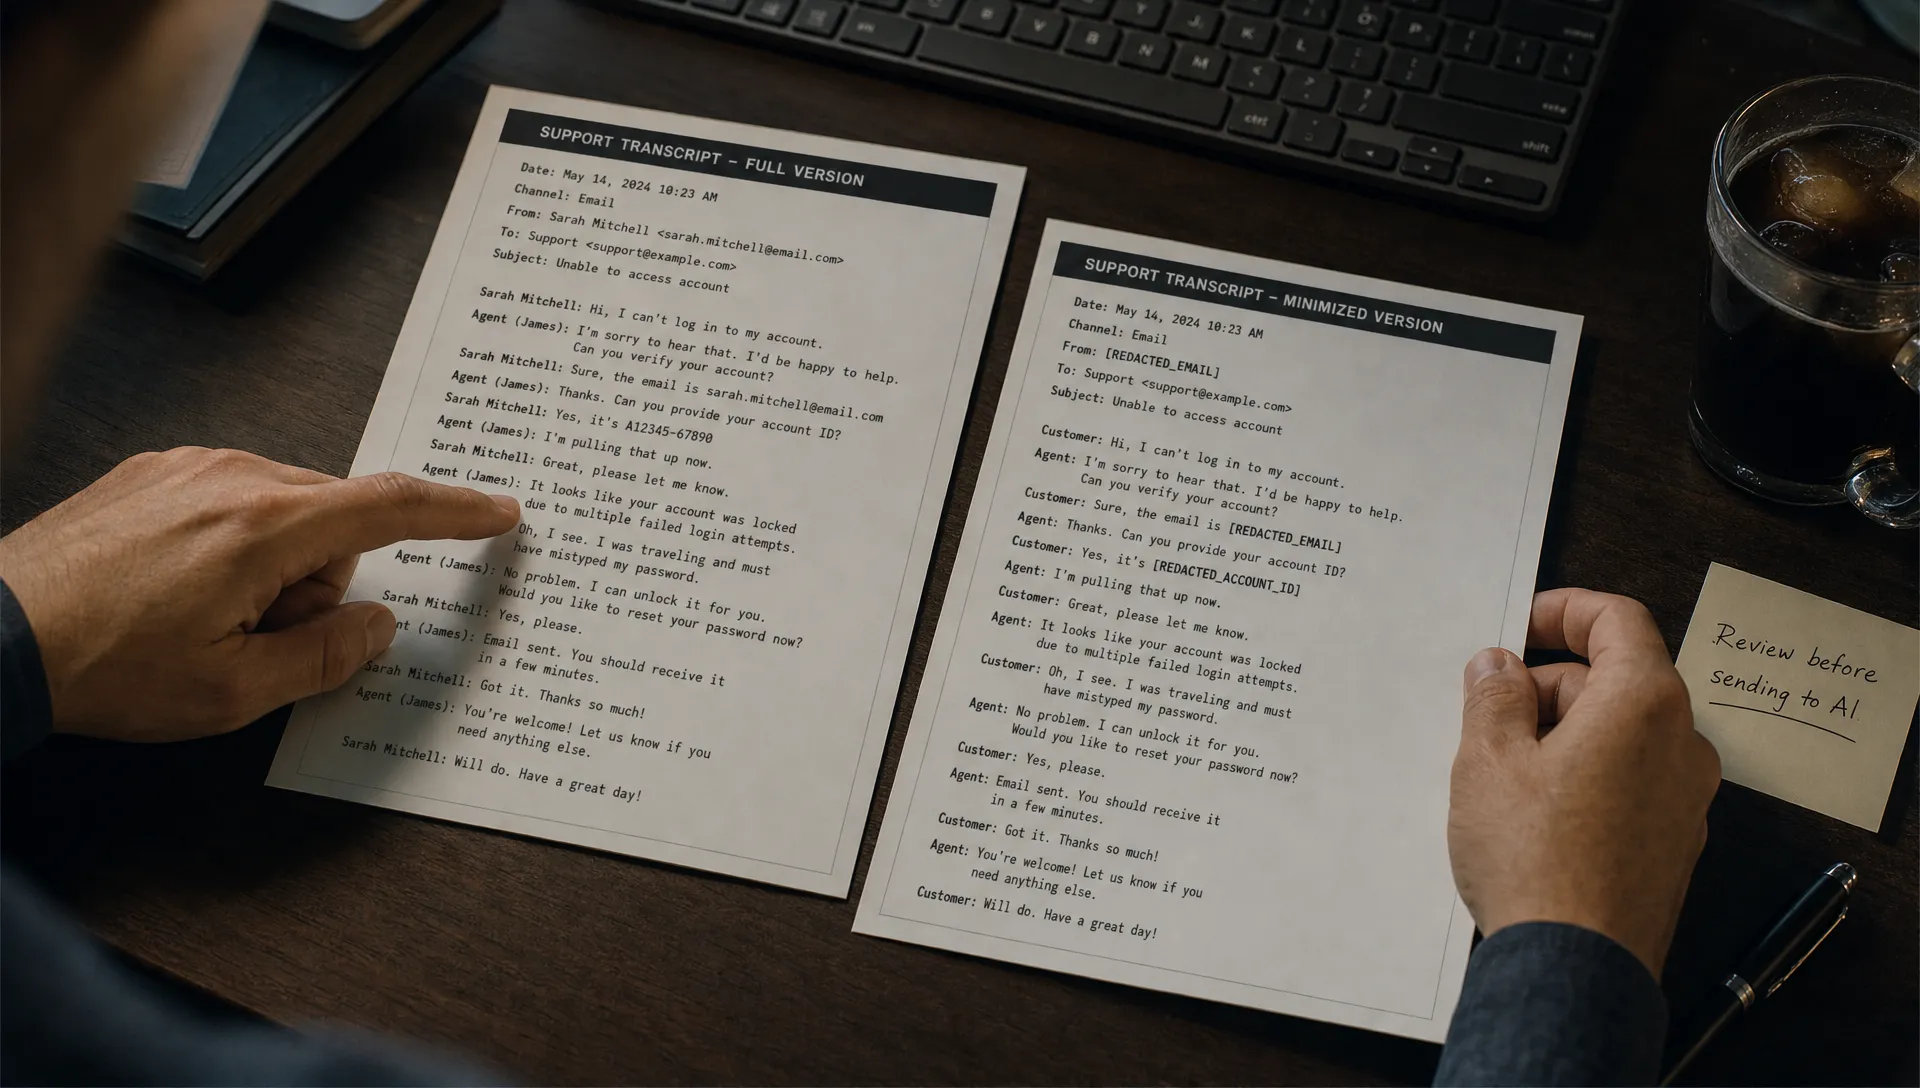
Consider a support agent drafting an escalation summary. The transcript contains the reproduction steps, but also a customer’s email address and billing notes. Copying everything preserves context. Selecting only the necessary details takes judgment and time.
Privacy language answers the wrong question
“Not used for training” does not, by itself, establish whether data is transmitted, retained or available to authorized reviewers. Those depend on the actual service configuration and agreements.
The NIST Generative AI Profile identifies data privacy as a risk category. Your interface should distinguish the relevant data-handling facts rather than compress them into “private.”
A user may understand your training policy perfectly and still misunderstand what they are allowed to submit.
Inspect the workflow without collecting another sensitive dataset
Run a task walkthrough using synthetic records that preserve the structure of real work. Include useful context mixed with fictional identifiers. Do not ask participants to demonstrate with live customer information in a research recording.
Observe the full sequence: choosing source material, copying it, reviewing the input and submitting it. Ask what participants expect to happen to the text at each point. Watch whether they notice the sensitive fields before a warning calls attention to them.
Trace the technical path separately. Does text leave the device through autosave, analytics, session replay or an input classifier before the user presses Send? A warning before model submission may still appear after data has crossed another boundary. Verify the sequence with engineering rather than inferring it from the interface.
Finally, remove unnecessary fields from the synthetic example and run the task again. If the output becomes unusable, determine which context was actually necessary. Otherwise, you risk prescribing redaction that users will bypass because it breaks their work.
Replace the risky shortcut with a usable path
Make the permitted input easier to assemble
For the support-summary task, offer a scoped selection of the relevant conversation rather than defaulting to the entire customer record. Exclude billing notes when they serve no purpose in the summary.
Where appropriate, provide a redacted preview with consistent placeholders so the conversation remains understandable. Explain where redaction happens. Server-side redaction still requires the original text to reach that server.
Redaction is not guaranteed anonymization. Free text can reveal identity through combinations of details, even after obvious identifiers disappear.
Give warnings a specific decision
“Do not share sensitive information” leaves the user to classify every field and repair the input alone.
A more actionable warning might say: “This text may contain an email address. Remove it before sending. The summary does not need contact details.” Offer the removal action and a reviewable preview, if your product supports them.
Use language that reflects detection uncertainty. A detector identifying a possible email address has not established that the entire document is safe or unsafe. Avoid turning a clean scan into a safety guarantee.
Enforce prohibited uses beyond the interface
If a data category is prohibited, an acknowledgment checkbox is not enforcement. Apply policy checks across supported entry points and validate before prohibited content reaches downstream processing. Client-side checks alone are bypassable.
Data loss prevention can support this boundary, but detection will miss some sensitive content and flag some permitted content. Pair it with input minimization and an approved alternative workflow.
Any review or exception route should follow organizational policy. A user clicking “continue anyway” does not create authorization.
Measure safe completion, not accepted warnings
Raw submission volume cannot tell you whether AI product adoption is healthy. Pair task completion with indicators of how users reached it.
Track the share of flagged attempts resolved through a permitted edit, the share abandoned after intervention and the completion rate through the approved path. Investigate whether blocks push work toward another input channel or an unapproved tool. Treat that displacement as a hypothesis until you have evidence.
Instrument the intervention, not the sensitive text. Prefer event categories, counts and resolution states over raw prompts or detected snippets. Review whether session replay and error reporting capture input contents.
Compare results within similar tasks and policy categories. A higher warning count could reflect broader detection coverage rather than riskier behavior. Fewer warnings could mean safer use or an easier bypass.
Frequently asked questions
Should we block every paste containing personal data? Not by default. The decision depends on permitted use, contractual commitments and the processing environment. Block prohibited handling, not every appearance of a name regardless of context.
Will a stronger disclaimer solve the problem? It may clarify expectations, but it does not remove workflow pressure. Test whether users can complete the task with permitted data after reading it.
Should we disable paste entirely? Only if the workflow justifies that restriction. Removing paste without a usable alternative may shift the same data into typing, attachments or another tool.
Choose one task and test the safer route
Pick one frequently pasted artifact. Define the minimum necessary context, map where its contents travel and test a permitted path against the current workflow. Success means users finish the task without crossing the prohibited boundary.
If the failure is still unclear, start with the free Triage tool. For a deeper team exercise, the AI Product Adoption Deck provides 12 diagnostics, 80 action cards across 10 stacks and 12 workshops in a 104-card, 124-page PDF. Use it to turn the observed break into a specific product decision, not another blanket warning.